
Updated Dec 24, 2023 NSE7_LED-7.0 Exam Dumps - PDF Questions and Testing Engine
New (2023) Fortinet NSE7_LED-7.0 Exam Dumps
The Fortinet NSE 7 - LAN Edge 7.0 certification exam covers a wide range of topics, including network design, routing, switching, wireless LANs, virtual private networks (VPNs), and network security. Candidates will be tested on their ability to plan, configure, and troubleshoot LAN Edge solutions using Fortinet products such as FortiGate, FortiSwitch, and FortiAP.
NEW QUESTION # 21
You are setting up an SSID (VAP) to perform RADlUS-authenticated dynamic VLAN allocation Which three RADIUS attributes must be supplied by the RADIUS server to enable successful VLAN allocation'' (Choose three.)
- A. Tunnel-Pvt-Group-ID
- B. Tunnel-Medium-Type
- C. Tunnel-Preference
- D. Tunnel-Type
- E. Tunnel-Private-Group-ID
Answer: B,D,E
Explanation:
Explanation
According to the FortiAP Configuration Guide, "To perform RADIUS-authenticated dynamic VLAN allocation, the RADIUS server must supply the following RADIUS attributes: Tunnel-Private-Group-ID, which specifies the VLAN ID to assign to the user. Tunnel-Type, which specifies the tunneling protocol used for the VLAN. The value must be 13 (VLAN). Tunnel-Medium-Type, which specifies the transport medium used for the VLAN. The value must be 6 (802). Therefore, options A, D, and E are true because they describe the RADIUS attributes that must be supplied by the RADIUS server to enable successful VLAN allocation.
Option B is false because Tunnel-Pvt-Group-ID is not a valid RADIUS attribute name, but rather a typo for Tunnel-Private-Group-ID. Option C is false because Tunnel-Preference is not a required RADIUS attribute for dynamic VLAN allocation, but rather an optional attribute that specifies the priority of the VLAN.
NEW QUESTION # 22
Refer to the exhibit.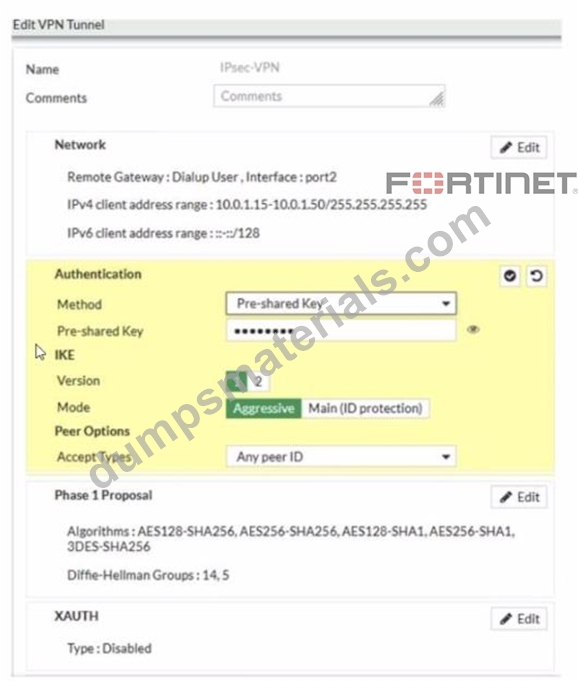
Examine the IPsec VPN phase 1 configuration shown in theexhibit
An administrator wants to use certificate-based authentication for an IPsec VPN user Which three configuration changes must you make on FortiGate to perform certificate-based authentication for the IPsec VPN user? (Choose three)
- A. In the Authentication section of the IPsec VPN tunnel in the Method drop-down list select Signature and then select the certificate that FortiGate will use for IPsec VPN
- B. Import the CA that signed the user certificate
- C. Create a PKI user for the IPsec VPN user, and then configure the IPsec VPN tunnel to accept the PKI user as peer certificate
- D. Enable XAUTH on the IPsec VPN tunnel
- E. In the IKE section of the IPsec VPN tunnel in the Mode field select Main (ID protection)
Answer: A,B,D
Explanation:
Explanation
According to the FortiGate Administration Guide, "To use certificate-based authentication, you must configure the following settings on both peers: Select Signature as the authentication method and select a certificate to use for authentication. Import the CA certificate that issued the peer's certificate. Enable XAUTH on the phase 1 configuration." Therefore, options B, D, and E are true because they describe the configuration changes that must be made on FortiGate to perform certificate-based authentication for the IPsec VPN user.
Option A is false because creating a PKI user for the IPsec VPN user is not required, as the user certificate can be verified by the CA certificate. Option C is false because changing the IKE mode to Main (ID protection) is not required, as the IKE mode can be either Main or Aggressive for certificate-based authentication.
NEW QUESTION # 23
Which two statements about FortiSwitchmanager are true1? (Choose two)
- A. Per-device management is the default management mode on FortiManager
- B. FortiManager obtains the FortiSwitch status information by querying the FortiGate REST API every three minutes
- C. Any switch discovered or authorized on FortiGate must be added manually on FortiSwitch manager
- D. If the administrator makes any changes on FortiSwitch manager they must also install those changes on FortiGate so that those changes are applied on the managed switches
Answer: B,D
Explanation:
Explanation
According to the FortiManager Administration Guide1, "FortiManager obtains the FortiSwitch status information by querying the FortiGate REST API every three minutes." Therefore, option B is true because it describes how FortiManager gets the information about the managed switches. According to the same guide2,
"If you make any changes in this module, you must install them on your managed device so that they are applied on your managed switches." Therefore, option C is true because it describes what the administrator must do after making any changes on FortiSwitch manager. Option A is false because central management is the default management mode on FortiManager, not per-device management. Option D is false because anyswitch discovered or authorized on FortiGate will be automatically added on FortiSwitch manager, not manually.
1: https://docs.fortinet.com/document/fortimanager/7.0.0/administration-guide/734537/fortiswitch-manager 2:
https://docs.fortinet.com/document/fortimanager/7.0.0/administration-guide/734537/fortiswitch-manager#fortisw
NEW QUESTION # 24
Which two pieces of information can the diagnose test authserver ldap command provide? (Choose two.)
- A. It displays whether the user credentials are correct
- B. It displays the LDAP codes returned by the LDAP server
- C. It displays whether the admin bind user credentials are correct
- D. It displays the LDAP groups found for the user
Answer: A,B
Explanation:
Explanation
According to the FortiGate CLI Reference Guide, "The diagnose test authserver ldap command tests LDAP authentication with a specific LDAP server. The command displays whether the user credentials are correct and whether the user belongs to any groups that match a firewall policy. The command also displays the LDAP codes returned by the LDAP server." Therefore, options B and C are true because they describe the information that the diagnose test authserver ldap command can provide. Option A is false because the command does not display whether the admin bind user credentials are correct, but rather whether the user credentials are correct. Option D is false because the command does not display the LDAP groups found for the user, but rather whether the user belongs to any groups that match a firewall policy.
NEW QUESTION # 25
A wireless network in a school provides guest access using a captive portal to allow unregistered users to self-register and access the network The administrator is requested to update the existing configuration to provide captive portal authentication through a secure connection (HTTPS) Which two changes must the administrator make to enforce HTTPS authentication"? (Choose two >
- A. Disable HTTP administrative access on the guest SSID to enforce HTTPS connection
- B. Create a new SSID with the HTTPS captive portal URL
- C. Enable HTTP redirect in the user authentication settings
- D. Update the captive portal URL to use HTTPS on FortiGate and FortiAuthenticator
Answer: C,D
Explanation:
Explanation
According to the FortiGate Administration Guide, "To enable HTTPS authentication, you must enable HTTP redirect in the user authentication settings. This redirects HTTP requests to HTTPS. You must also update the captive portal URL to use HTTPS on both FortiGate and FortiAuthenticator." Therefore, options B and D are true because they describe the changes that the administrator must make to enforce HTTPS authentication for the captive portal. Option A is false because creating a new SSID with the HTTPS captive portal URL is not required, as the existing SSID can be updated with the new URL. Option C is false because disabling HTTP administrative access on the guest SSID will not enforce HTTPS connection, but rather block HTTP connection.
NEW QUESTION # 26
Refer to the exhibit.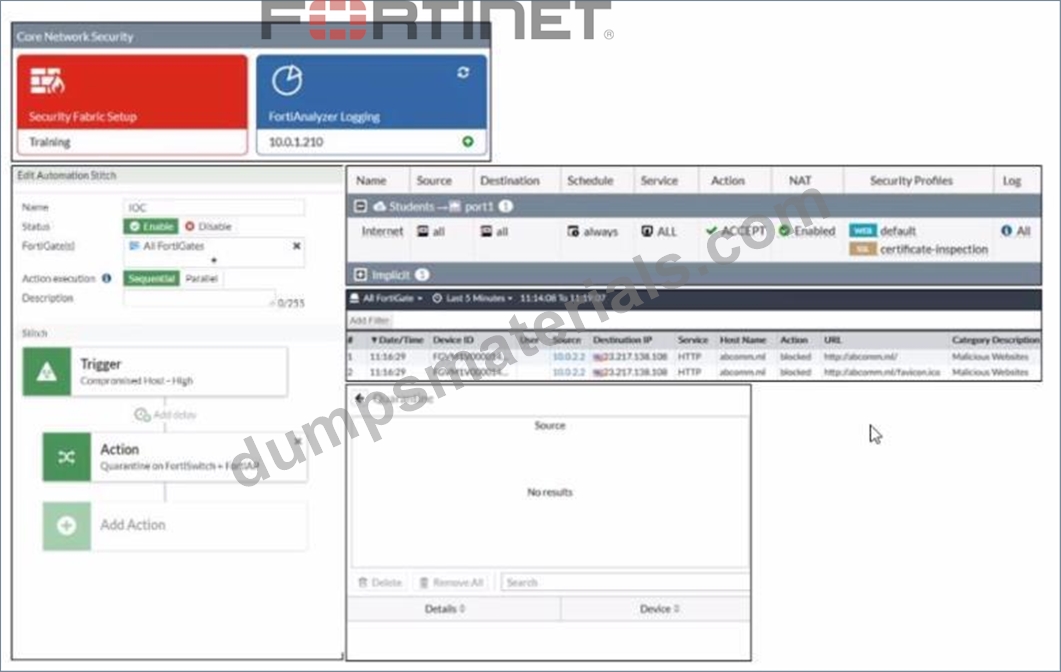
Examine the FortiGate configuration FortiAnalyzer logs and FortiGate widget shown in the exhibit An administrator is testing the Security Fabric quarantine automation The administrator added FortiAnalyzer to the Security Fabric and configured an automation stitch to automatically quarantine compromised devices The test device (::.:.:.!) s connected to a managed Fort Switch dev :e After trying to access a malicious website from the test device, the administrator verifies that FortiAnalyzer has a log (or the test connection However the device is not getting quarantined by FortiGate as shown in the quarantine widget Which two scenarios are likely to cause this issue? (Choose two)
- A. The device does not have FortiClient installed
- B. The web filtering rating service is not working
- C. FortiAnalyzer does not have a valid threat detection services license
- D. FortiAnalyzer does not consider the malicious website an indicator of compromise (IOC)
Answer: C,D
Explanation:
Explanation
According to the exhibits, the administrator has configured an automation stitch to automatically quarantine compromised devices based on FortiAnalyzer's threat detection services. However, according to the FortiAnalyzer logs, the test device is not detected as compromised by FortiAnalyzer, even though it tried to access a malicious website. Therefore, option B is true because FortiAnalyzer does not have a valid threat detection services license, which is required to enable the threat detection services feature. Option D is also true because FortiAnalyzer does not consider the malicious website an indicator of compromise (IOC), which is a criterion for identifying compromised devices. Option A is false because the web filtering rating service is working, as shown by the log entry that indicates that the test device accessed a URL with a category of
"Malicious Websites". Option C is false because the device does not need to have FortiClient installed to be quarantined by FortiGate, as long as it is connected to a managed FortiSwitch device.
NEW QUESTION # 27
Which FortiSwitch VLANs are automatically created on FortGate when the first FortiSwitch device is discovered1?
- A. access, quarantine, rspan. voice, video, and onboarding
- B. default quarantine, rspan voice video onboarding and nac_segment
- C. default quarantine rspan voice video and nac_segment
- D. fortilink. quarantine erspan voice video and onboarding
Answer: D
Explanation:
Explanation
According to the FortiGate Administration Guide, "When you add a FortiSwitch device to the Security Fabric, FortiGate automatically creates the following VLANs on theFortiSwitch device: fortilink, quarantine, erspan, voice, video, and onboarding." Therefore, option D is true because it lists the FortiSwitch VLANs that are automatically created on FortiGate when the first FortiSwitch device is discovered. Option A is false because default and nac_segment are not among the automatically created VLANs. Option B is false because access and rspan are not among the automatically created VLANs. Option C is false because default and nac_segment are not among the automatically created VLANs.
NEW QUESTION # 28 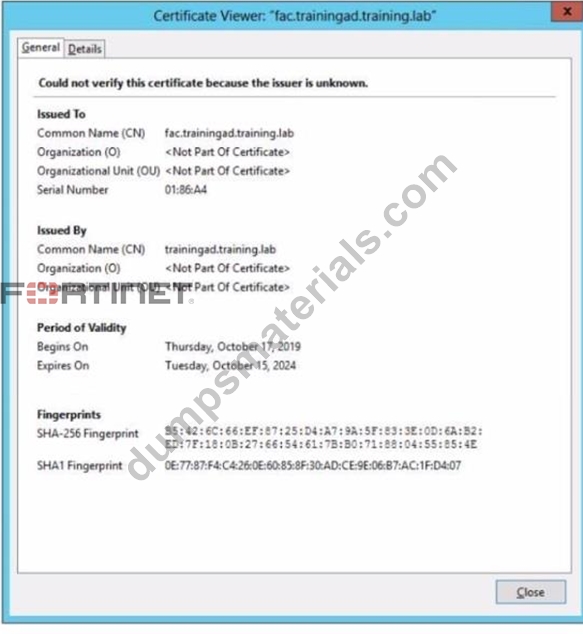
Wireless guest users are unable to authenticate because they are getting a certificate error while loading the captive portal login page.This URL string is the HTTPS POST URL guest wireless users see when attempting to access the network using the web browser
Which two settings are the likely causes of the issue? (Choose two.)
- A. The user address is not in DDNS form
- B. The wireless user's browser is missing a CA certificate
- C. The FortiGate authentication interface address is using HTTPS
- D. The external server FQDN is incorrect
Answer: B,D
Explanation:
Explanation
According to the exhibit, the wireless guest users are getting a certificate error while loading the captive portal login page. This means that the browser cannot verify the identity of the server that is hosting the login page.
Therefore, option A is true because the external server FQDN is incorrect, which means that it does not match the common name or subject alternative name of the server certificate. Option B is also true because the wireless user's browser is missing a CA certificate, which means that it does not have the root or intermediate certificate that issued the server certificate. Option C is false because the FortiGate authentication interface address is using HTTPS, which is a secure protocol that encrypts the communication between the browser and the server. Option D is false because the user address is not in DDNS form, which is not related to the certificate error.
NEW QUESTION # 29
Which two statements about the guest portal on FortiAuthenticator are true? (Choose two.)
- A. Administrators must approve all guest accounts before they can be used
- B. The guest portal provides pre and post-log in services
- C. Administrators can use one or more incoming parameters to configure a mapping rule for the guest portal
- D. Each remote user on FortiAuthenticator can sponsor up to 10 guest accounts
Answer: B,C
Explanation:
Explanation
According to the FortiAuthenticator Administration Guide2, "The guest portal provides pre and post-log in services for users (such as password reset and token registration abilities), and rules and replacement messages can be configured." Therefore, option C is true. The same guide also states that "Administrators can use one or more incoming parameters to configure a mapping rule for the guest portal." Therefore, option D is true.
Option A is false because remote users can sponsor any number of guest accounts, as long as they do not exceed the maximum number of guest accounts allowed by the license. Option B is false because administrators can choose to approve or reject guest accounts, or enable auto-approval.
NEW QUESTION # 30
Refer to the exhibit.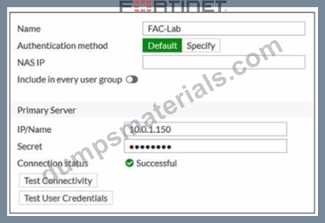
Examine the RADIUS server configuration shown in the exhibit
An administrator has configured a RADIUS server on FortiGate that points to FortiAuthenticator FortiAuthenticator is acting as an authentication proxy and is configured to relay all authentication requests to a remote Windows AD server using LDAP While testing the configuration the administrator noticed that the diagnosetest authserver command worked with PAP, however authentication requests failed when using MSCHAP2 Which two solutions can the administrator implement to get MSCHAP2 authentication to work'' (Choose two.)
- A. On FortiAuthenticator change the back-end authentication server from LDAP to RADIUS
- B. On FortiGate configure the NAS IP setting on the RADIUS
server - C. On FortiAuthenticator enable Windows Active Directory Domain Authentication to add FortiAuthenticator to the Windows domain
- D. On FortiGate update the Secret setting on the RADIUS server
Answer: A,C
Explanation:
Explanation
According to the exhibit, the RADIUS server configuration on FortiGate points to FortiAuthenticator, which is acting as an authentication proxy and is configured to relay all authentication requests to a remote Windows AD server using LDAP. However, LDAP does not support MSCHAP2 authentication, which is required for RADIUS. Therefore, option A is true because on FortiAuthenticator, enabling Windows Active Directory Domain Authentication will add FortiAuthenticator to the Windows domain and allow it to use MSCHAP2 authentication with the AD server. Option C is also true because on FortiAuthenticator, changing the back-end authentication server from LDAP to RADIUS will allow it to use MSCHAP2 authentication with the AD server. Option B is false because on FortiGate, configuring the NAS IP setting on the RADIUS server will not affect the MSCHAP2 authentication, but rather the source IP address of the RADIUS packets. Option D is false because on FortiGate, updating the Secret setting on the RADIUS server will not affect the MSCHAP2 authentication, but rather the shared secret between FortiGate and FortiAuthenticator.
NEW QUESTION # 31
Refer to the exhibit.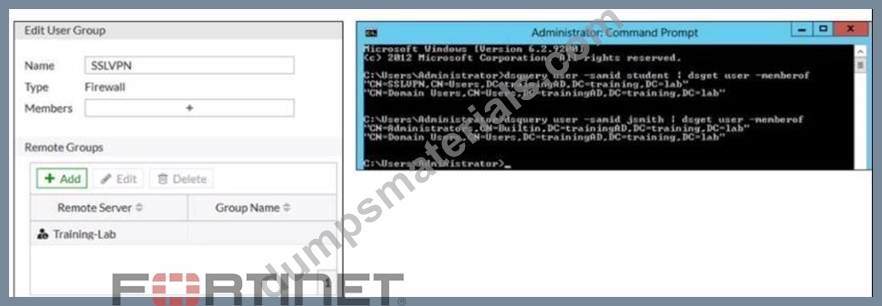
Examine the FortiGate user group configuration and the Windows AD LDAP group membership information shown in the exhibit FortiGate is configured to authenticate SSL VPN users against Windows AD using LDAP The administrator configured the SSL VPN user group for SSL VPN users However the administrator noticed that both the student and j smith users can connect to SSL VPN Which change can the administrator make on FortiGate to restrict the SSL VPN service to the student user only?
- A. In the SSL VPN user group configuration change Type to Fortinet Single Sign-On (FSSO)
- B. In the SSL VPN user group configuration set Group Nam to CN-SSLVPN, CN="users, DC-trainingAD, DC-training, DC-lab
- C. In the SSL VPN user group configuration, change Name to cn=sslvpn, CN=users, DC=trainingAD, Detraining, DC-lab.
- D. In the SSL VPN user group configuration set Group Name to ::;=Domain users.CN-Users/DC=trainingAD, DC-training, DC=lab.
Answer: B
Explanation:
Explanation
According to the FortiGate Administration Guide, "The Group Name is the name of the LDAP group that you want to use for authentication. The name must match exactly the name of the LDAP group on the LDAP server." Therefore, option A is true because it will set the Group Name to match the LDAP group that contains only the student user. Option B is false because changing the Name will not affect the authentication process, as it is only a local identifier for the user group on FortiGate. Option C is false because setting the Group Name to Domain Users will include all users in the domain, not just the student user. Option D is false because changing the Type to FSSO will require a different configuration method and will not solve the problem.
NEW QUESTION # 32
Exhibit.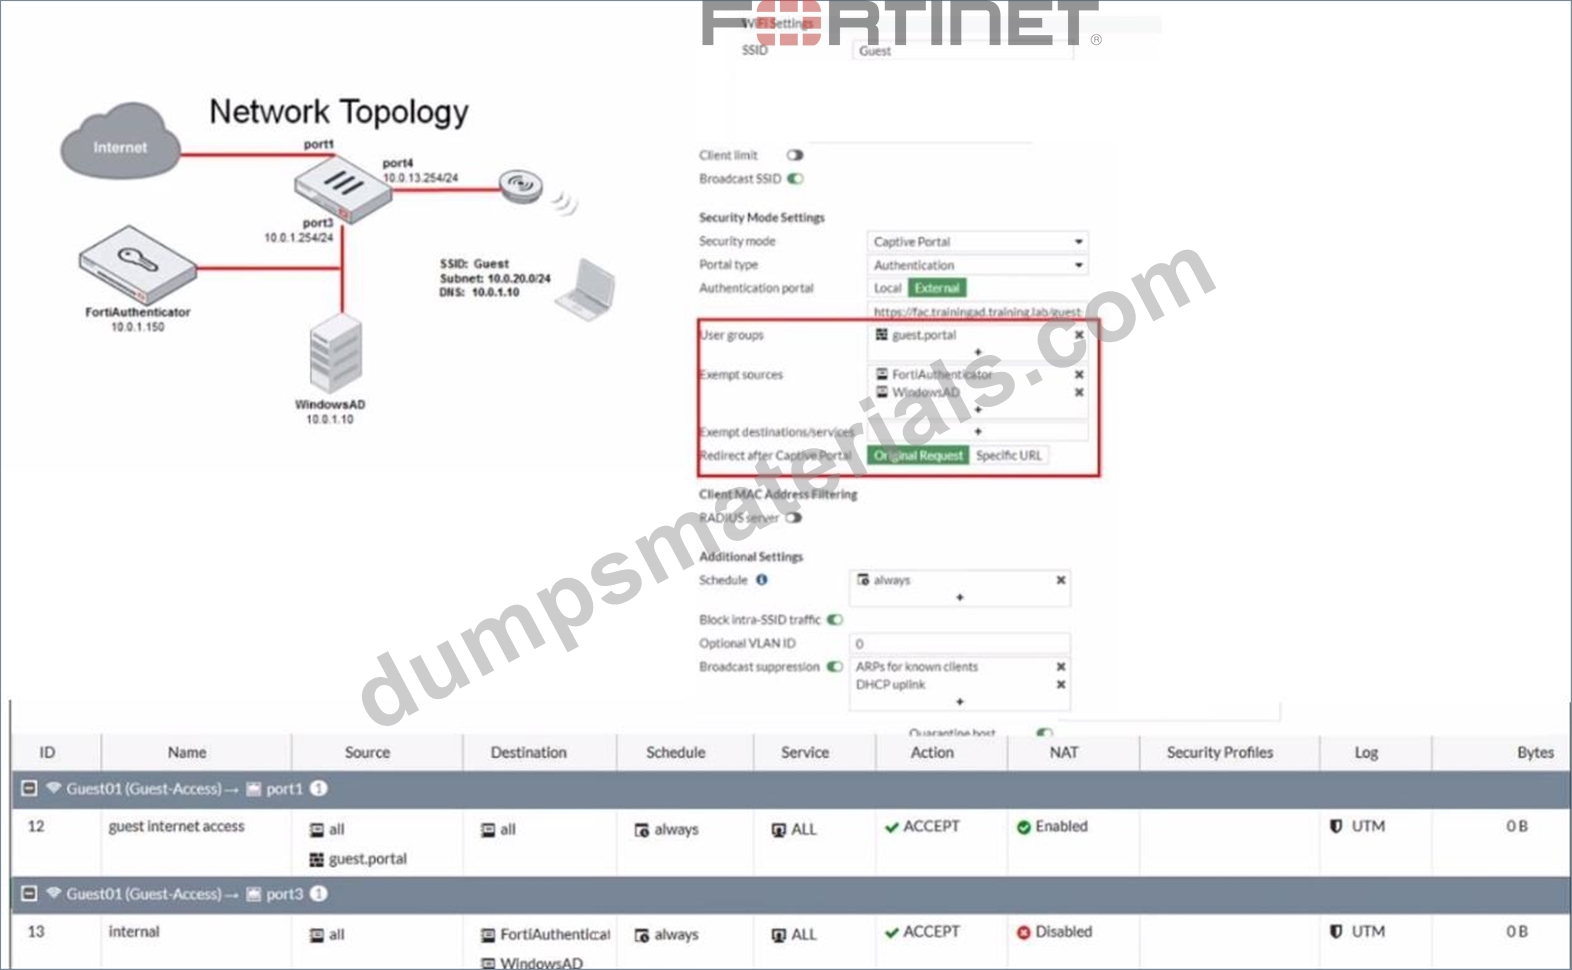
Refer to the exhibit showing a network topology and SSID settings.
FortiGate is configured to use an external captive portal However wireless users are not able to see the captive portal login page Which configuration change should the administrator make to fix the problem?
- A. Enable NAT in the firewall policy with the ID 13.
- B. Add the FortiAuthenticator and WindowsAD address objects as exempt destinations services
- C. Remove the guest.portal user group in the firewall policy with the ID 12
- D. Enable the captive-portal-exempt option in the firewall policy with the ID 12
Answer: B
Explanation:
Explanation
According to the exhibit, the network topology and SSID settings show that FortiGate is configured to use an external captive portal hosted on FortiAuthenticator, which is connected to a Windows AD server for user authentication. However, wireless users are not able to see the captive portal login page, which means that they are not redirected to the external captive portal URL. Therefore, option B is true because adding the FortiAuthenticator and WindowsAD address objects as exempt destinations services will allow the wireless users to access the external captive portal URL without being blocked by the firewall policy. Option A is false because enabling NAT in the firewall policy with the ID 13 will not affect the redirection to the external captive portal URL, but rather the source IP address of the wireless traffic. Option C is false because enabling the captive-portal-exempt option in the firewall policy with the ID 12will bypass the captive portal authentication for the wireless users, which is not the desired outcome. Option D is false because removing the guest.portal user group in the firewall policy with the ID 12 will prevent the wireless users from being authenticated by FortiGate, which is required for accessing the external captive portal.
NEW QUESTION # 33
Which CLI command should an administrator use to view the certificate verification process in real time?
- A. diagnose debug application foauthd -1
- B. diagnose debug application authd -1
- C. diagnose debug application radiusd -1
- D. diagnose debug application fnbamd -1
Answer: A
Explanation:
Explanation
According to the FortiOS CLI Reference Guide, "The diagnose debug application foauthd command enables debugging of certificate verification process in real time." Therefore, option A is true because it describes the CLI command that an administrator should use to view the certificate verification process in real time. Option B is false because diagnose debug application radiusd -1 enables debugging of RADIUS authentication process, not certificate verification process. Option C is false because diagnose debug application authd -1 enables debugging of authentication daemon process, not certificate verification process. Option D is false because diagnose debug application fnbamd -1 enables debugging of FSSO daemon process, not certificate verification process.
NEW QUESTION # 34
Refer to the exhibit.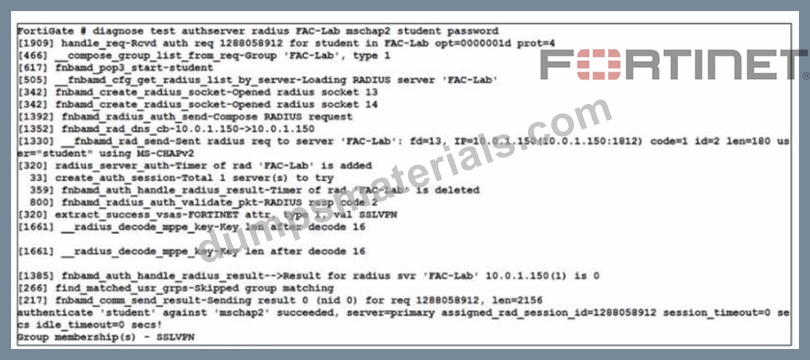
Examine the debug output shown in the exhibit
Which two statements about the RADIUS debug output are true'' (Choose two)
- A. User authentication failed
- B. The RADIUS server sent a vendor-specific attribute in the RADIUS response
- C. The user student belongs to the SSLVPN group
- D. User authentication succeeded using MSCHAP
Answer: C,D
Explanation:
Explanation
According to the exhibit, the debug output shows a RADIUS debug output from FortiGate. The output shows that FortiGate sent a RADIUS Access-Request packet to FortiAuthenticator with the username student and received a RADIUS Access-Accept packet from FortiAuthenticator with a Class attribute containing SSLVPN.
Therefore, option A is true because it indicates that the user student belongs to the SSLVPN group on FortiAuthenticator. The output also shows that FortiGate used MSCHAP as the authentication method and received a MS-MPPE-Send-Key and a MS-MPPE-Recv-Key from FortiAuthenticator. Therefore, option D is true because it indicates that user authentication succeeded using MSCHAP. Option B is false because user authentication did not fail, but rather succeeded. Option C is false because FortiAuthenticator did not send a vendor-specific attribute in the RADIUS response, but rather standard attributes defined by RFCs.
NEW QUESTION # 35
Refer to the exhibit.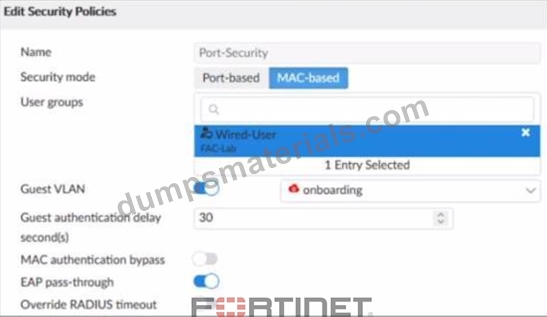
Examine the FortiSwitch security policy shown in the exhibit
If the security profile shown in the exhibit is assigned to all ports on a FortiSwitch device for 802 1X authentication which statement about the switch is correct?
- A. FortiSwitch will try to authenticate non-802 1X devices using the device MAC address as the username and password
- B. All EAP messages will be terminated on FortiSwitch
- C. FortiSwitch cannot authenticate multiple devices connected to the same port
- D. FortiSwitch will assign non-802 1X devices to the onboarding VLAN
Answer: D
Explanation:
Explanation
According to the FortiSwitch Administration Guide, "If a device does not support 802.1X authentication, you can configure the switch to assign the device to an onboarding VLAN. The onboarding VLAN is a separate VLAN that you can use to provide limited network access to non-802.1X devices." Therefore, option C is true because it describes the behavior of FortiSwitch when the security profile shown in the exhibit is assigned to all ports. Option A is false because FortiSwitch can authenticate multiple devices connected to the same port using MAC-based or MAB-EAP modes. Option B is false because FortiSwitch will not try to authenticate non-802.1X devices using the device MAC address as the username and password, but rather use MAC authentication bypass (MAB) or EAP pass-through modes. Option D is false because all EAP messages will be terminated on FortiGate, not FortiSwitch, when using 802.1X authentication.
NEW QUESTION # 36
An administrator is testing the connectivity for a new VLAN The devices in the VLAN are connected to a FortiSwitch device that is managed by FortiGate Quarantine is disabled on FortiGate While testing the administrator noticed that devices can ping FortiGate and FortiGate can ping the devices The administrator also noticed that inter-VLAN communication works However intra-VLAN communication does not work Which scenario is likely to cause this issue?
- A. The FortiSwitch MAC address table is missing entries
- B. The native VLAN configured on the ports is incorrect
- C. The FortiGate ARP table is missing entries
- D. Access VLAN is enabled on the VLAN
Answer: A
Explanation:
Explanation
According to the scenario, the devices in the VLAN are connected to a FortiSwitch device that is managed by FortiGate. Quarantine is disabled on FortiGate, which means that the devices are not blocked by any security policy. The devices can ping FortiGate and FortiGate can ping the devices, which means that the IP connectivity is working. Inter-VLAN communication works, which means that the routing between VLANs is working. However, intra-VLAN communication does not work, which means that the switching within the VLAN is not working. Therefore, option C is true because the FortiSwitch MAC address table is missing entries, which means that the FortiSwitch does not know how to forward frames to the destination MAC addresses within the VLAN. Option A is false because access VLAN is enabled on the VLAN, which means that the VLAN ID is added to the frames on ingress and removed on egress. This does not affect intra-VLAN communication. Option B is false because the native VLAN configured on the ports is incorrect, which means that the frames on the native VLAN are not tagged with a VLAN ID. This does not affect intra-VLAN communication. Option D is false because the FortiGate ARP table is missing entries, which means that FortiGate does not know how to map IP addresses to MAC addresses. This does not affect intra-VLAN communication.
NEW QUESTION # 37
......
Fortinet NSE7_LED-7.0 exam is the latest iteration in the Fortinet NSE 7 certification program, which aims to certify IT professionals on how to design, implement, and manage secure LAN edge solutions. NSE7_LED-7.0 exam is specifically designed for network administrators, IT managers, and security professionals who want to validate their skills in deploying and managing Fortinet’s Secure SD-WAN, SD-Branch, and LAN edge solutions.
Updated Verified Pass NSE7_LED-7.0 Exam - Real Questions and Answers: https://www.dumpsmaterials.com/NSE7_LED-7.0-real-torrent.html
Best Way To Study For Fortinet NSE7_LED-7.0 Exam Brilliant NSE7_LED-7.0 Exam Questions PDF: https://drive.google.com/open?id=1cDdsT_hyPwFjsbk8MBw0dbmyc023o4oB
